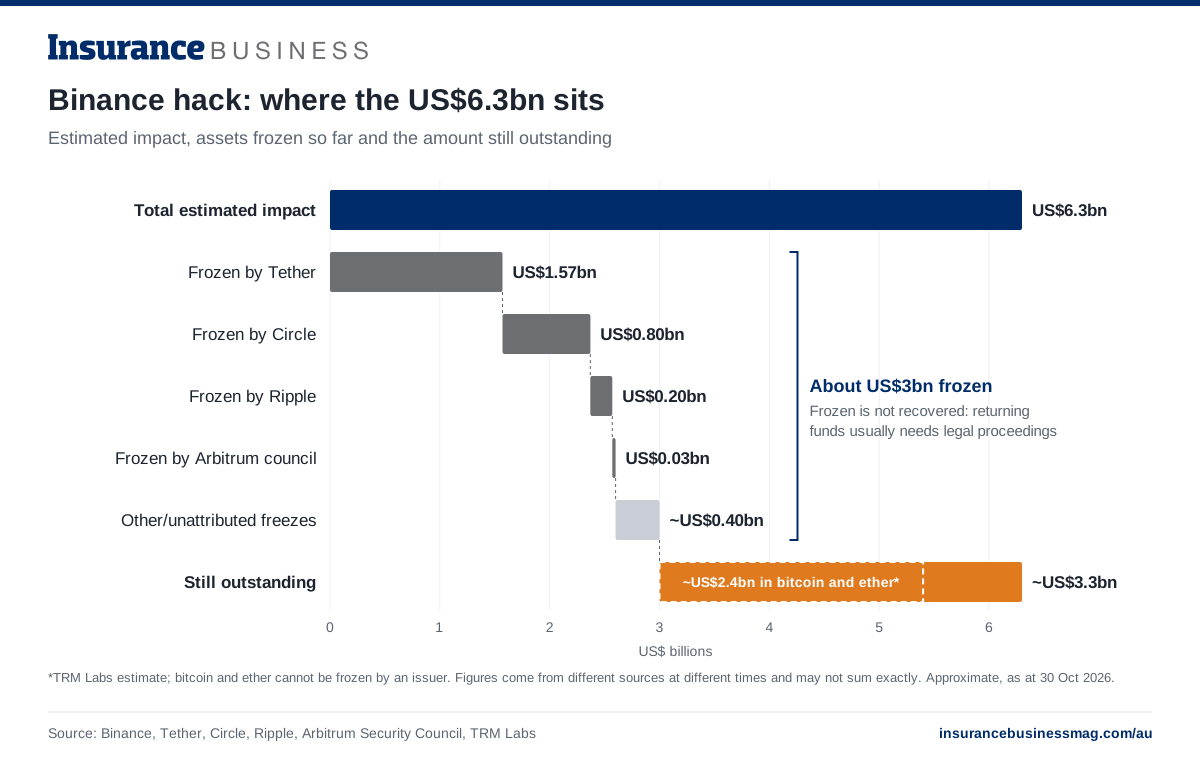
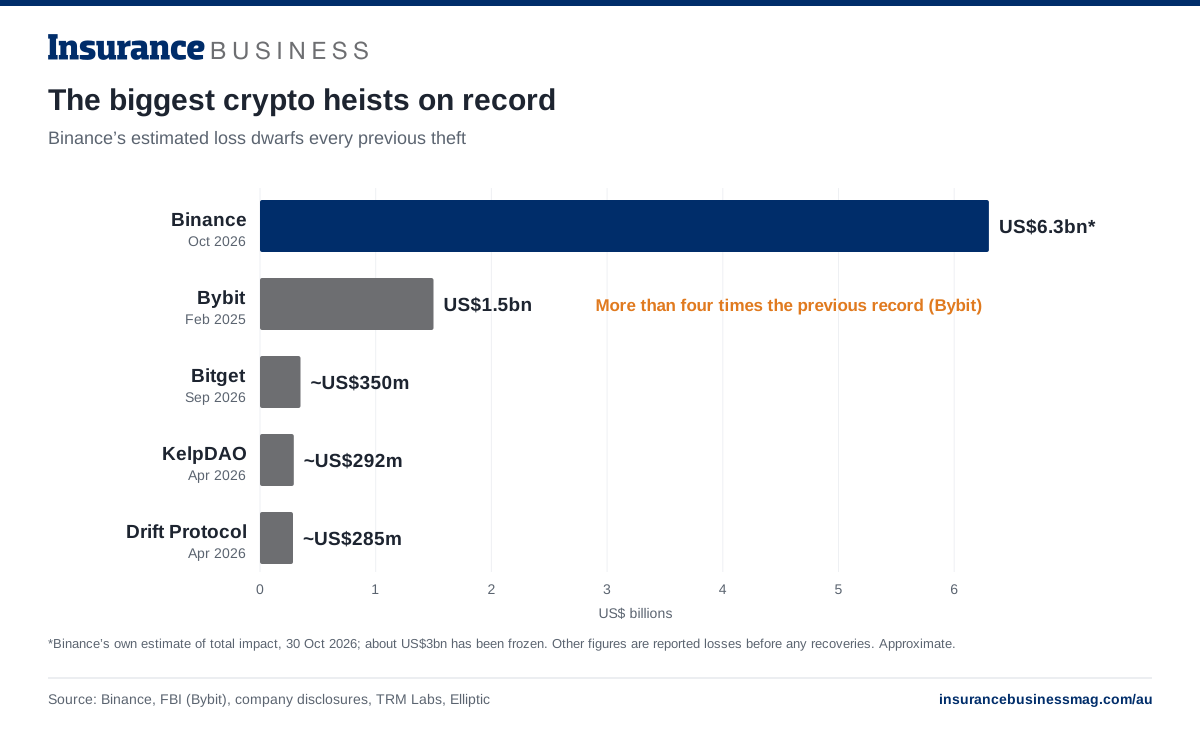
Binance has frozen deposits and withdrawals for its 335 million users while it investigates a breach it now puts at US$6.3 billion. That is more than four times the previous record for a crypto theft.
The exchange paused withdrawals at around 9.15am AEDT today, as users reported funds draining from its hot wallets. “It does look like a hack on Binance,” co-founder Changpeng Zhao posted on X shortly afterwards.
Binance’s preliminary investigation points to one compromised laptop belonging to a DevOps engineer. The exchange says the attacker used the laptop to reach an internal service and submit unauthorised withdrawals. Binance says it has found no evidence that wallet private keys were leaked, although at least one security firm has questioned that account. Binance has promised to cover all losses from its Secure Asset Fund for Users (SAFU) and from company funds. Withdrawals will stay suspended until its security checks are complete.
Read next: ASIC’s urgent letter puts insurers and brokers on notice: AI has changed the cyber threat landscape
Binance is paying for this loss itself. SAFU was set up in 2018 and is owned and managed by the exchange. It is held entirely in bitcoin and is worth roughly US$1 billion to US$1.2 billion, depending on the coin’s price. That covers less than a fifth of the estimated loss, so the rest has to come from Binance’s balance sheet.
Binance has done this before, on a much smaller scale. In 2019 it covered a US$40 million bitcoin theft from its own funds and kept withdrawals shut for about a week. Today’s loss is more than 150 times larger.
Specialist crypto insurers such as Evertas have expanded capacity this year, and WTW has bought its way into the market. Even so, nothing in the specialist market’s publicly reported capacity comes even close to a single loss of this size.
Freezing funds also does not mean recovering them. Redbord told CNBC that getting frozen stablecoins back to their owners usually requires legal proceedings, and there is no standard timeline.
Read next: Gallagher rolls out insurance to safeguard Australian fintechs in crypto space
The North Korean link raises a question about exclusions. Under Lloyd’s Market Bulletin Y5381, standalone cyber policies written at Lloyd’s since 31 March 2023 must exclude war and certain state-backed attacks. The bulletin focuses on attacks that significantly impair a state’s ability to function or its security capabilities. It also requires policies to set out how an attack will be attributed. A theft from a private exchange looks hard to bring within that test. However, wordings differ, and claims teams will read their clauses closely before relying on any exclusion.
The way the attacker got in is also familiar. Last month the Australian Cyber Security Centre and international partners warned that North Korean operators are targeting IT professionals with fake job offers in order to compromise their machines.
Read next: Organized fraud is outgrowing Asia-Pacific’s cyber insurance market
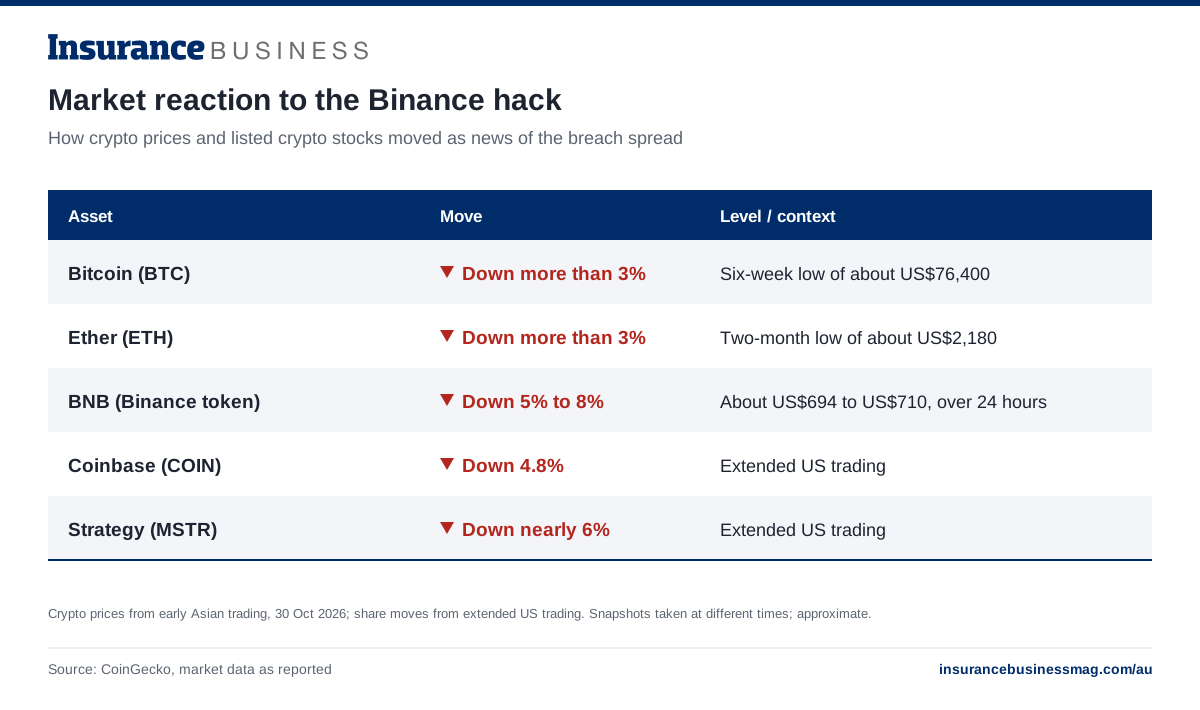
This attack follows Bitget’s loss of roughly US$350 million in September. TRM Labs says North Korea-linked groups took about 76% of all crypto hack value in the first four months of this year.
Tim Sun, senior researcher at Hong Kong’s HashKey Group, told Reuters the breach could prompt investors to reassess counterparty, solvency and liquidity risk at centralised exchanges. Kevin March, co-founder of JPEG Trading, told The Wall Street Journal he expects the loss to be manageable for Binance. Very few exchanges could absorb a loss on this scale.
Read next: AI as a risk amplifier: how cyber insurance is evolving