This story is developing and will be updated.
Cyber agencies across ANZ and the Asia-Pacific have issued urgent warnings over two critical flaws in PHP, the code behind most of the world’s websites. Attackers began targeting the flaws within hours of them becoming public.
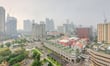
The Australian Signals Directorate’s Australian Cyber Security Centre (ACSC) issued a critical alert, its highest rating, and told organisations to find every instance of PHP running in their environments. The agency said its own website, cyber.gov.au, was among the Australian government sites affected.
Singapore’s Cyber Security Agency published an alert of its own, warning that the flaws affect all versions of PHP. In Japan, Prime Minister Sanae Takaichi addressed the issue publicly. Several Japanese services were taken offline as a precaution, including childcare centre systems and online games.
The flaws are tracked as CVE-2026-109618 and CVE-2026-109619 and nicknamed “PHP2Shell”. They can let an attacker take control of a web server without logging in. Both are rated 9.2 out of 10 for severity.
PHP’s developers released fixes at 14:00 UTC on 21 October, in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35, available from php.net. That was late on Wednesday night across most of Asia, and in the early hours of Thursday in Australia and New Zealand. The release was brought forward after details leaked online a day earlier.
PHP builds a web page each time someone visits it, pulling product listings, account details or login screens from a database and sending the result to the browser. It is free, maintained largely by volunteers, and sits underneath WordPress, Drupal, Magento and many hosting platforms. Australia’s GovCMS, which hosts many federal government websites, is built on Drupal. Because the flaws are in PHP itself, a website can be exposed even if its own code is sound.
Security firm watchTowr says its network of decoy servers has recorded attempts to exploit both flaws. No breach at a real organisation had been confirmed by the time the fixes were released. However, exploit code is circulating publicly, and the Dutch national cyber agency says it expects large-scale attacks soon.
Europe also moved quickly. Government agencies in the Netherlands, Finland and France took websites offline, as did parts of Wikipedia.
Read next: HK and Singapore’s regulators both warned this. Top financial watchdog just confirmed it
The bugs were found by security firms Calif and Wiz, both using frontier AI models. OpenAI, whose model Calif used, called them “one of the most impactful security issues in recent memory”. Wiz said the weaknesses had been sitting in PHP’s code for decades.
Web technology tracker W3Techs puts PHP’s share at around 70% of websites whose server-side language it can identify. Only versions 8.2 to 8.5 have official fixes. Sites still running older releases have no simple update to install.
The region has been caught out by PHP before. A separate critical flaw disclosed in 2024 was actively exploited against systems in Japan, Singapore and the US, and Singapore’s Cyber Security Agency later confirmed attacks were under way.
PHP2Shell is the kind of event cyber underwriters model but rarely see: one piece of shared software that could expose thousands of policyholders at the same moment. The region’s insurers would face it with prices still falling.
Marsh’s latest Global Insurance Market Index, published this week, shows Pacific cyber rates fell 8% in the third quarter, a steeper drop than the 6% recorded in the previous quarter. Globally, cyber rates fell 4%, the thirteenth consecutive quarterly decline. Marsh had already noted that Pacific claims frequency was rising, with a large share of notifications linked to supply chain events.
In Asia, the bigger concern is how little of the exposure is insured. Swiss Re estimates Asia-Pacific accounts for about 10% of global cyber premium, or roughly US$1.56 billion, which it considers small relative to the region’s digital exposure. Cover among small and medium-sized businesses in Asia sits below the global average of around 10%. Many of the firms most exposed to PHP2Shell, such as small businesses with ageing websites on budget hosting, are the least likely to have cover.
Read next: Organized fraud is outgrowing Asia-Pacific’s cyber insurance market
Brokers should expect questions about business interruption, especially from clients who took their own websites offline as a precaution. Whether a policy responds will depend on its wording and waiting period, and few policies explicitly cover voluntary shutdowns.
Clients whose websites run on a provider’s shared servers depend on that provider to patch. If the provider goes down, the client’s loss falls under contingent business interruption. That cover isn’t standard and often carries a sub-limit. Underwriters may also want to know how quickly clients patched once a fix was available.
For clients, the first job is finding out who manages PHP on their website and getting written confirmation that it has been updated. They should also check whether their insurer has sent a vulnerability alert. With attacks under way, any server that was left unpatched should be checked for signs of a break-in, and anything suspicious reported to the insurer promptly. Australian organisations that suspect they have been affected can contact the ACSC on 1300 CYBER1 (1300 292 371).
Read next: Singapore telco breach signals turning point for cyber insurance
Insurance Business will update this story as it develops.