Two critical vulnerabilities in PHP, the programming language behind a large share of the world’s websites, have led governments and businesses across several countries to take websites offline.
Claims specialists now expect a wave of cyber notifications, though the eventual insured loss remains unclear.
The flaws, tracked as CVE-2026-109618 and CVE-2026-109619 and nicknamed “PHP2Shell,” can allow unauthenticated remote code execution on web servers. Both carry a critical CVSS score of 9.2. PHP released fixes on October 21 in versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35, a day earlier than planned after details leaked online.
The US Cybersecurity and Infrastructure Security Agency (CISA) urged organizations to patch immediately, prioritizing internet-facing systems. It advised taking PHP-based systems offline if they could not be updated right away or were running unsupported versions. The UK’s National Cyber Security Centre gave similar advice. CISA said it had not seen successful exploitation when it published its alert.
In the Netherlands, government services including DigiD and MijnOverheid went offline as a precaution, and organizations in other countries did the same. On October 23, PHP disclosed a third remote code execution vulnerability, CVE-2026-115560, according to CERT-EU, with full details due in a later release.
Global claims management firm Crawford & Company said the scale of the exposure could drive a sharp rise in cyber incident notifications, precautionary inquiries and claims activity. However, the eventual insured loss will depend on how far the flaws are exploited, the disruption that results, and the terms of individual policies.
Crawford said businesses were already commissioning forensic investigations and incident response, and filing notices of potential claim, even where no compromise or loss has been confirmed.
“The key claims distinction is between precautionary action and a confirmed cyber incident,” said Robert Holmes, an executive general adjuster with Crawford in Canada. Holmes said taking systems offline to patch them does not automatically mean a covered loss has occurred, and that policy triggers, waiting periods and security conditions all need careful assessment.
Crawford expects business interruption to be the main claims issue for many organizations. Where systems are taken down briefly to apply patches, waiting periods and the need for a covered security event may limit recovery. Larger losses are more likely where attackers exploit the flaws, leading to system compromise, data exposure or prolonged disruption.
Policy conditions on minimum security standards, vulnerability management, timely patching and the use of unsupported or legacy software may also affect coverage decisions. Where hosting, infrastructure or patching has been outsourced, questions over who was responsible could lead to professional liability claims against service providers and subrogation claims by insurers.
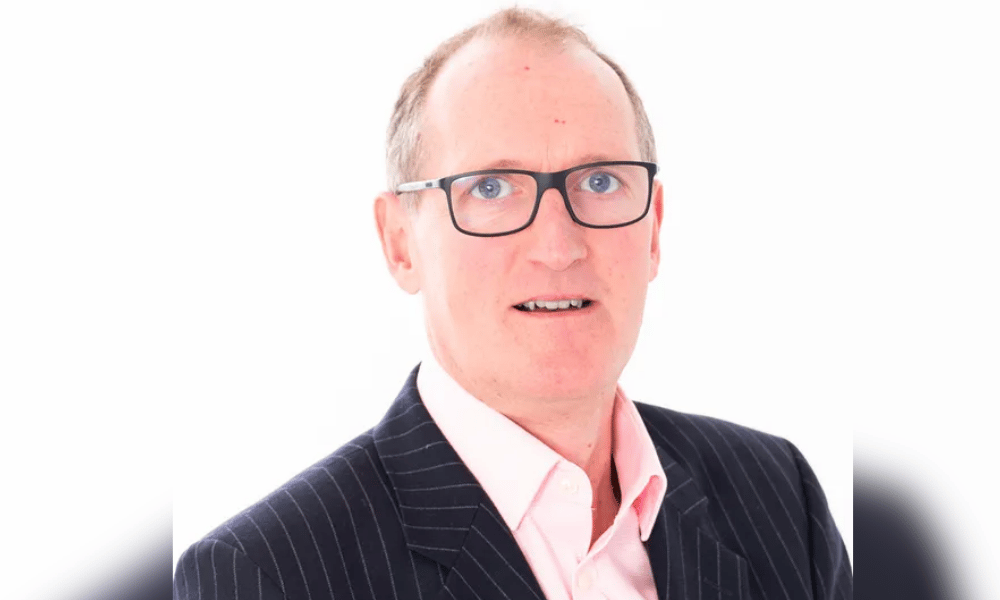
Paul Handy (pictured), Crawford’s global head of cyber, said a flaw in widely used technology can quickly become a cross-sector, multi-jurisdictional event, highlighting how concentrated risk has become in shared digital infrastructure.
The event follows similar warnings from industry bodies. The Insurance Bureau of Canada’s latest cyber report identified shared technology dependencies as a growing source of correlated losses. Moody’s Ratings has also said that advances in AI could increase cyber risk by speeding up how quickly software vulnerabilities are found and exploited.
For brokers, the immediate priority is client guidance. Clients should document their patching and any shutdowns, notify insurers in line with policy requirements, and avoid assuming that a precautionary outage will be covered. Once the event settles, how insurers treat precautionary costs and security conditions is likely to shape cyber wordings and renewal questions for many years.