New Zealand workers started Friday 13 November without Outlook, Teams or Copilot. A Microsoft 365 failure that began on Thursday afternoon US time rolled straight into the local working day.
The disruption reached well beyond inboxes, ABC News reported in Australia. Councils in regional NSW announced closures of Service NSW centres, and some Sydney councils' customer service systems were affected. In western Queensland, Western Meat Exporters director Campbell McPhee said the business had gone "old school", phoning suppliers and customers because its orders normally run through email. The School of the Air in Longreach cancelled online lessons for students on sheep and cattle stations. In Adelaide, business owner Bronte Hough said he couldn't process orders, print invoices or make deliveries.
Critical services have largely held up. The Australian Energy Market Operator said there was no disruption to the energy systems and markets it runs, and the Bureau of Meteorology said its forecasts and warnings were unaffected, as was the AusAlert national warning system. The ABC found no direct impact on frontline police, court operations or Sydney Airport.
Ali Yavari, an associate professor at Swinburne University of Technology, told ABC News the bigger concern was what staff would do next. "Out of frustration or urgency, employees may turn to personal email accounts, unmanaged devices or unapproved messaging and file-sharing services to keep working," he said. Once sensitive information moves outside an organisation's security controls, he said, the result can be unauthorised disclosure, loss of oversight and privacy or confidentiality breaches. "Those consequences can outlast the outage itself."
The services Microsoft listed as potentially affected included several Microsoft Purview tools, among them data loss prevention and communication compliance, as well as Defender for Office 365 and Intune, according to the ABC. Many organisations rely on those tools to detect sensitive data leaving the business. For part of the outage, some of them may not have worked properly while staff were improvising.
Some workers had few options. ABC readers said codes for two-factor authentication into other business apps arrived by email, locking them out of systems that had nothing to do with Microsoft. One reader who said they worked in family violence services said their client database, which is linked to Outlook, was out of reach.
Scammers have seen an opportunity and have moved quickly as well. ING has warned customers of fraudsters that might contact them offering to fix Microsoft problems, and told them not to let anyone access their devices without first checking through the organisation's published phone number. The office of the home affairs minister said National Cyber Security Coordinator Lieutenant General Michelle McGuinness was aware of the outage and looking into it.
Read next: Shadow AI risk widens as governance frameworks lag behind
Microsoft said the problem was not a surge in traffic but a large number of servers going offline unexpectedly, which shifted their load onto the rest of the system, according to its Microsoft 365 Status account on X. A Microsoft spokesperson told the ABC there was "no indication this is a cyber attack."
Recovery has been uneven. Microsoft brought some servers back using an alternative health check method, then said that servers which returned in good health stopped responding again once they started handling traffic. It said it was rebuilding a subset of servers with a previous software configuration and examining whether a small number of recent configuration updates had contributed.
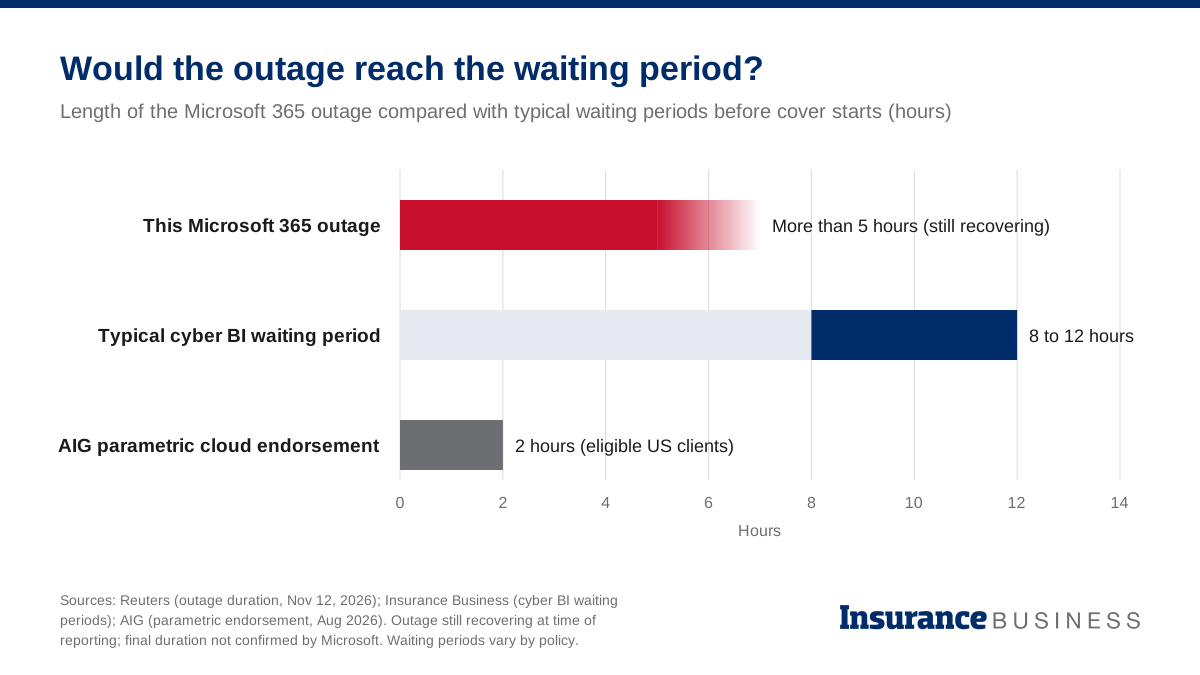
Reports of Outlook problems on Downdetector peaked at 138,058 and the disruption had run for more than five hours by Thursday evening in the US, Reuters reported. Downdetector said nearly seven in 10 reports came from the United States, according to the ABC. As of publication, Microsoft had not published a root cause or confirmed full restoration. Administrators can follow incidents EX1550543 and MO1550821 in the Microsoft 365 admin centre or on the public cloud status page.
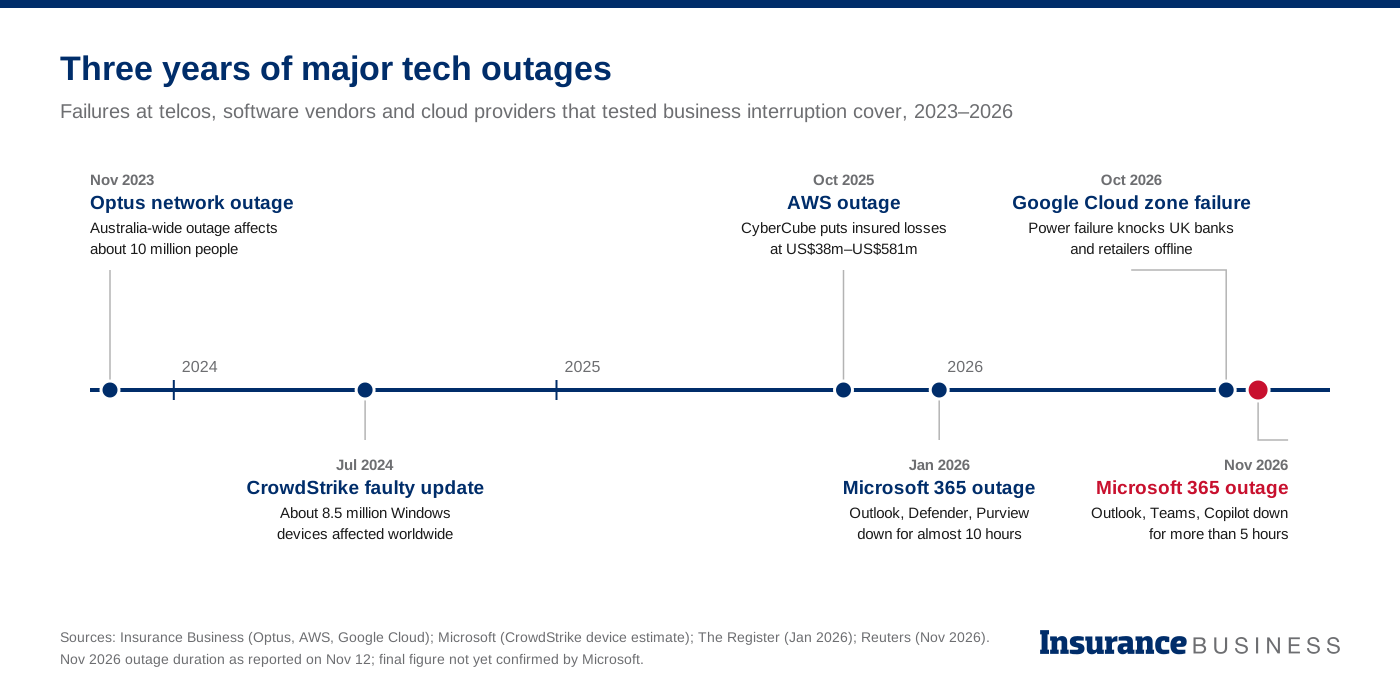
Yavari said the outage showed how heavily organisations depend on shared infrastructure, where one provider's failure can reach businesses worldwide. "We saw the consequences of shared technology dependencies during the CrowdStrike outage in July 2024, when a faulty security software update affected an estimated 8.5 million Windows devices," he said.
Read next: Australian firms face growing outage losses their insurance may not cover
For brokers, a data leak caused by a workaround and a loss caused by the outage are separate problems that may fall under different parts of a cyber policy. A client file forwarded to a personal Gmail account can be a privacy incident in its own right. Under the Privacy Act's Notifiable Data Breaches scheme, organisations covered by the Act must notify affected individuals and the OAIC when a breach is likely to result in serious harm, and must assess a suspected breach promptly. For APRA-regulated clients, the prudential standard on operational risk, CPS 230, also expects them to manage disruption at material service providers.
Underwriters were already aware that unapproved tools were an issue. More than 80% of workers use AI tools their employer has not approved, according to UpGuard research on shadow AI. Gallagher's John Farley has said AI use "brings the potential to trigger multiple insurance policies," naming cyber, D&O, professional liability and employment practices liability among them. An outage that pushes staff from Copilot to a free chatbot adds to that exposure. How a policy responds may also depend on what the insured told underwriters about its controls, and whether staff followed them on the day. That will vary by wording.
On business interruption, the length of this outage matters. Cyber BI cover typically starts only after eight to 12 hours of downtime. An outage that ran more than five hours, and was still recovering well into Friday morning in Australia, came closer to that line than many recent cloud failures, though insureds would still need losses beyond the waiting period.
When Optus's network failed in November 2023, insurance lawyers warned that business interruption cover would be limited for most affected businesses. Wordings have moved since: some carriers are restructuring contingent business interruption language around IT and non-IT vendors, and some limit cover to named vendors, according to IB's reporting on the ADS cyberattack. Emergence's updated SME wording, for example, offers full-limit cover for system failure. Many businesses have no cyber cover at all: the Australian Institute of Criminology recorded cyber insurance take-up among those it surveyed falling to 3.7% from 4.6%.
Read next: ADS cyberattack tests whether supply chain policies actually respond
Yavari said businesses need approved alternative ways to communicate and "clear guidance about what information can be shared, ensuring staff can keep working securely when their usual tools are unavailable."
That gives brokers a practical agenda for client calls. Ask whether staff were told what to do when email went down or were left to improvise. Find out whether any client, patient or financial data moved to personal accounts or unapproved apps during the outage. If it did, assess it under the Notifiable Data Breaches scheme and talk to the insurer early. Check whether multi-factor authentication depends on the same email system it is meant to protect. Keep a record of downtime, lost staff hours and failed transactions in case a business interruption claim becomes viable.
Read next: Cyber costs surge as Australian businesses lag on crisis readiness
The broader issue is concentration. A continuity plan that moves staff from Outlook to Teams offers no backup when both run on the same Microsoft infrastructure, and Friday showed how many Australian organisations, from state agencies to meatworks, sit on that one platform.
This story may be updated as Microsoft releases more details on the cause and duration of the outage.