A single stolen credential has opened a route into hundreds of unrelated businesses in under a fortnight and the question it leaves behind is one that cyber wordings answer differently: whether those losses are one event or many.
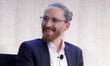
Mark Luckin (pictured), national manager for the cyber and technology sector at Lockton Companies Australia, said the answer sits in the contract rather than the incident.
“From a policy wording perspective, the starting point is the connection between the losses and the language used to combine them,” Sydney based Luckin told Insurance Business, speaking generally rather than about any specific compromise.
The issue recently came into focus concerning the ConnectWise Cloud Backup, formerly SkyKick, a tool used by managed service providers (MSPs) to back up client email, files and Teams data. In a report published on 21 October 2026, Microsoft attributed the attack to a China state-aligned group it tracks as Storm-0940, which used an AI penetration testing framework called ARTEX “to reach more than 2,250 tenants at 2,900 sign-in attempts per minute, a pace that leaves defenders with little time to detect and respond”. Most attempts failed. In several cases the group moved from first targeting an organisation to privileged access over its cloud infrastructure in under three hours.
Aggregation clauses decide whether related losses are treated as a single claim. “Some wordings group matters sharing the same originating or underlying source or cause into a single claim, even where different claimants, insured entities or events are involved under that policy,” Luckin said. Others treat related liability claims as one claim and related first-party incidents as one incident.
Which applies can cut both ways. “Aggregation can protect a business from repeated excesses for related losses, but can also mean those losses share an applicable limit,” he said. “Related-loss provisions may also determine which policy year responds.”
A supplier's policy and its customers' policies answer the question separately. Numerous customer claims against a technology provider arising from the same breach may be treated as a single claim under that provider's own policy, Luckin said, while the affected customers' claims under their own cyber policies are assessed on their own terms.
“The aggregation provisions do not automatically combine unrelated policyholders' contracts into one shared limit,” he said.
One endorsement can override the rest. “We would also examine any widespread or systemic event endorsement, because that can change the applicable cover, limits or excess when unrelated organisations are affected,” Luckin said.
Read next: Australian firms face growing outage losses their insurance may not cover
AXA XL's Vicky Sheridan flagged the underlying trend in Insurance Business's 2026 5-Star Cyber report: “We're also seeing growing exposure to cyber risks arising from third-party technology providers.”
The ConnectWise backup tool holds wide access to the Microsoft 365 environments it protects. Attackers stole the tool's own credential and used it to sign in as the application itself, sidestepping passwords and multi-factor checks.
Huntress, the security firm that first identified the activity, confirmed unauthorised sign-ins at 162 tenants by 16 October 2026, and has since identified close to 1,000 tenants that received sign-in attempts, more than 300 of them showing successful attempts. In some cases, Microsoft said, the AI agents changed credentials to keep access and altered admin roles. Microsoft has not said how many organisations were breached, and a successful sign-in does not establish that data was taken. Targeted sectors included aerospace and defence, energy, financial services, government, legal, manufacturing and semiconductors.
Storm-0940 has been active since 2021 and has historically relied on password spraying and OAuth application abuse. What is new is the pace. Microsoft says several groups now use ARTEX, and executive vice president Igor Tsyganskiy called the ConnectWise attack “one of many” in a wave of AI-driven attacks since early October 2026. The framework's developer took it closed source after researchers linked it to attacks on South Korean financial institutions, though copies already downloaded remain in circulation.
Read next: Perth arrests reveal the supply chain blind spot in Australian cyber cover
ConnectWise disabled the affected application identities on 17 October 2026 and completed a full reset of all accounts and credentials in the Cloud Backup environment on 19 October, according to its security advisories. Cloud Backup, SaaS Security and Cloud Management all remain suspended, with no restoration date confirmed as at 22 October. The company says a phased restoration will take several days once it begins, and that it has no indication backup archives were accessed.
That second exposure runs alongside the first. With backups offline for a ninth day, affected clients cannot restore data. Cover for a supplier's outage is often sublimited, and Allianz puts typical cyber business interruption indemnity periods at 90 to 180 days.
Does the client's IT provider use ConnectWise Cloud Backup or SkyKick? If so, has it reviewed sign-in logs across the period Microsoft identified? Where data was accessed, privacy notification rules and policy conditions apply, so the insurer should hear early.
Then the contract. Does the policy respond to a breach originating in a supplier's software? Is contingent business interruption included, and at what sublimit? How does the aggregation clause define a single claim, and does a widespread or systemic event endorsement sit over the top of it?
The same questions apply to any firm's own IT arrangements.
There is an irony in the detail. ConnectWise has promoted itself as a path to cyber cover for MSPs, partnering in 2022 with broker Ukon, formerly FifthWall Solutions, which said it worked with more than 35 insurers. Whether those policies were written for a week like this is now a live question.