Business interruption cover can appear in a cyber policy as network interruption or material interruption. Breach response costs might be called emergency costs, event management or crisis containment.
That variety sits behind a debate over whether cyber wordings should be standardised. Most voters in an IBUK LinkedIn poll said insurers should be left to compete, while just one backed standardising only triggers and loss calculations, the middle ground suggested in an interview on why cyber policies can look identical until a claim.
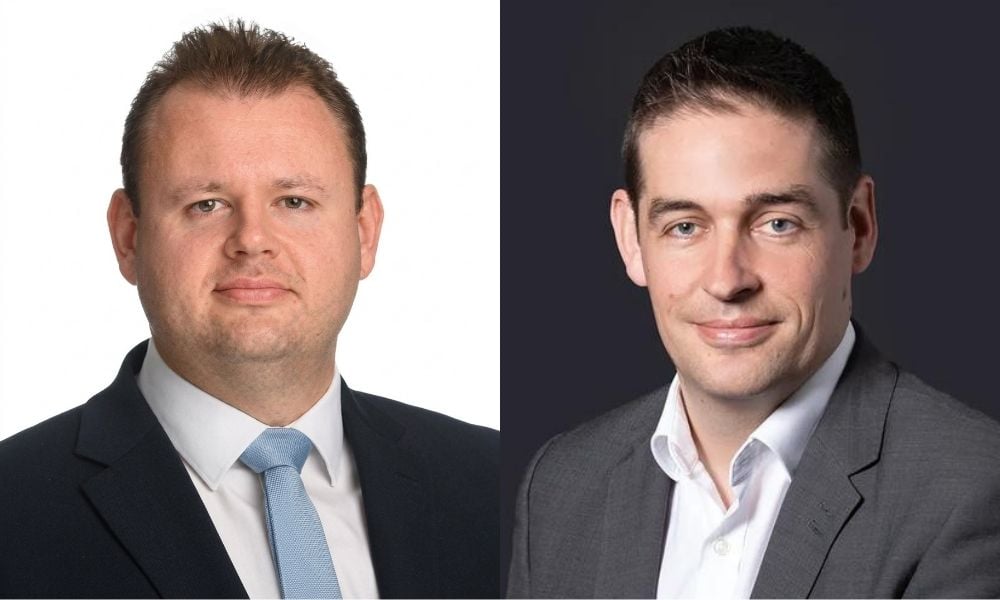
Daniel Johnson (pictured top, left), class underwriter, cyber at AEGIS London, said liability cover can also be labelled privacy liability or network security liability. Insurers are not the only ones using their own definitions: brokers and vendors do too.
Differentiation can benefit clients, he said, but has pitfalls when buyers do not understand the wording or coverage. He regularly hears of clients choosing the cheapest option, even though a lower price usually comes at the expense of cover.
"This is the crux of it for me: brokers having the appropriate level of knowledge to review, compare, and explain differences in cyber wordings – it comes down to training and awareness throughout the insurance placement chain," he said.
Tim Johnson (pictured top, right), partner and head of the insurance practice at Browne Jacobson, said it was hard to call one approach good and the other bad. He compared cyber with employers' liability, where regulations largely set out what a policy has to cover. That gives buyers greater certainty, but leaves less flexibility, with specialist risks having to go to specialist markets.
"With cyber, I think standardisation would be too difficult because a cyber policy for a small one-person owner-managed business working from their spare bedroom with a laptop will be entirely different from an aviation business with 1,000 planes in the skies all over the world at any one moment in time," he said.
In his personal view, insurers and commercial buyers should retain the freedom to negotiate terms rather than have specific language mandated. The ability to assess risks differently, price them accordingly and tailor wordings is one of the keys to the London market's strength in bespoke and unusual risks, he said.
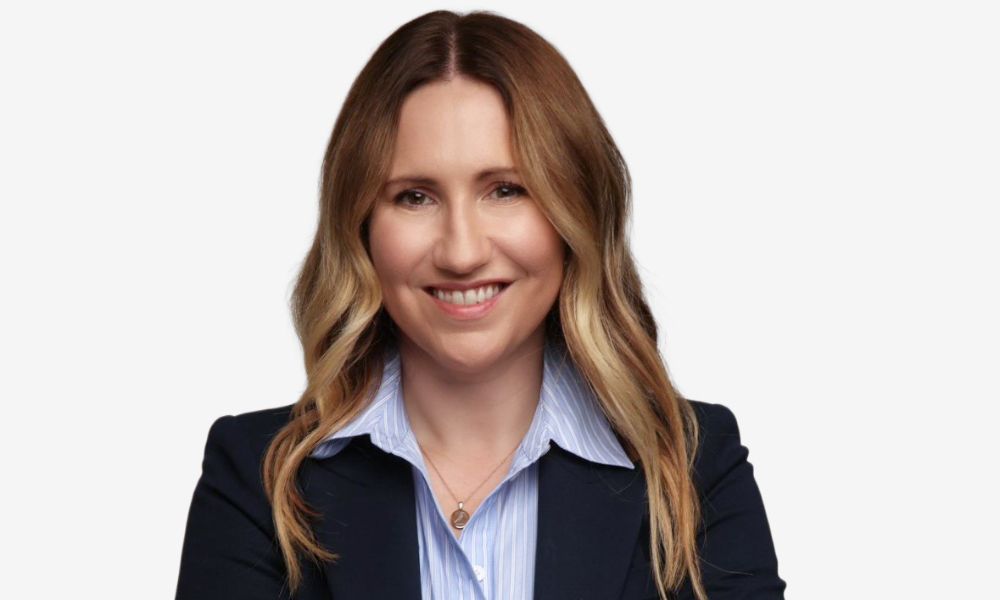
Insurers make the same case. Lindsey Maher (pictured, immediately above), head of global cyber development at CFC, which recently added executive protection and affirmative AI wording to its cyber policy, said standardisation risks solving the wrong problem in one of insurance's fastest-moving risk environments, where insurers need the freedom to evolve cover as technology, threats and client needs change.
"If we standardise wordings too heavily, we risk standardising the market around yesterday's risks," Maher said.
Tim Johnson acknowledged that flexibility has a cost when insurers describe what is nominally the same risk in different ways.
"If you've got two different insurers using two different sets of language, then the inevitable consequence of that is potentially more disputes," he said.
Daniel Johnson said he would personally welcome some standardisation around common definitions to make cyber policies easier to understand.
"I believe differentiation is required to allow for innovation, but for such a complex product, common definitions should be standardised," he said.
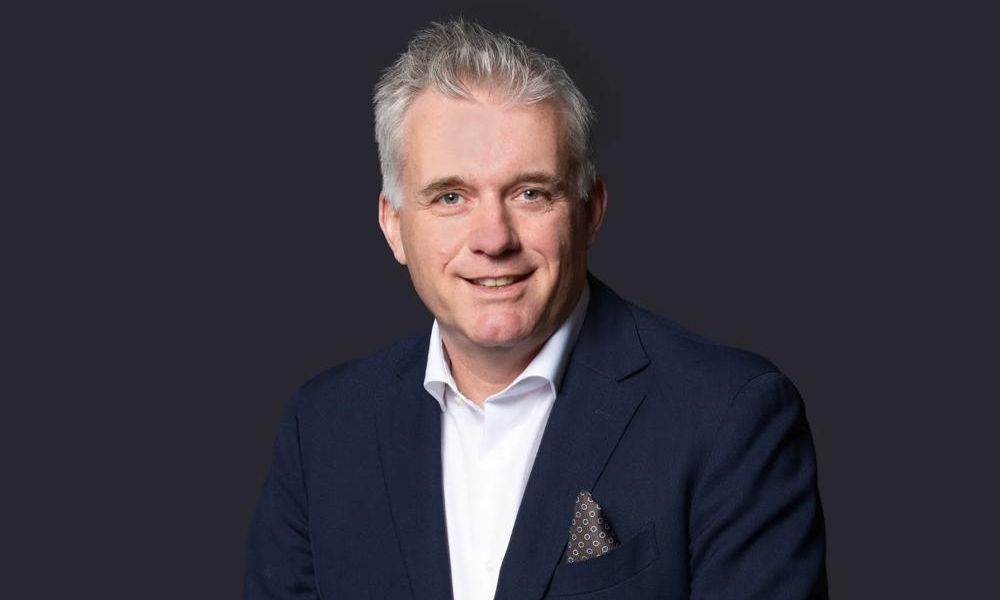
Technology could also help with comparisons. Philip James (pictured immediately above), partner and head of UK data, privacy and cybersecurity at Browne Jacobson, said AI can analyse multiple policy wordings quickly.
"AI could take 10, 20, 30 policy wordings and actually do a fairly quick analysis of the various wordings in it," James said.
He said that gives brokers and customers more ability to compare policies, leaving less room to argue that a buyer did not know what they were buying.
Tim Johnson said wordings were becoming clearer, a shift that began before Consumer Duty and has gained focus through it, driven by insurers wanting to do the right thing and competition in a soft market. He sees education as a bigger barrier to businesses buying the right cyber cover than complicated wordings or insufficient coverage.
A cyber policy can combine six to nine different covers in various permutations, he said, so it cannot be reduced to a one-page summary, even as cyber has moved from something of a luxury a decade ago to one of a business’s core covers.
Most poll voters favoured leaving insurers to compete on wordings. That leaves brokers with the task Daniel Johnson identified: understanding the differences well enough to explain what a client gains, or gives up, when choosing a policy.