Cyber insurance buyers continue to benefit from falling premiums and abundant capacity, but growing concerns over third-party technology dependencies are prompting some insurers to tighten coverage even as competition for clients remains intense.
US cyber insurance rates declined by 2% in the second quarter of 2026, matching the previous quarter's decrease, according to Marsh's latest Global Insurance Market Index. Rates have been falling since the second quarter of 2023, while global cyber premiums declined by 4%, marking the twelfth consecutive quarter of reductions.
But the favorable pricing environment comes as businesses face increasingly interconnected cyber exposures. Verizon's 2026 Data Breach Investigations Report found that third parties were involved in 48% of analyzed breaches, a 60% increase from the previous year's dataset. Marsh also identified third-party software and vendor risks among insurers' leading concerns, despite stable cyber capacity and continuing competition.
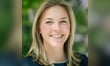
According to Megan North (pictured), executive vice president and branch leader at Amwins, some insurers are introducing widespread-event exclusions and restricting dependent business interruption coverage to manage their exposure to failures involving critical technology providers.
“The sheer nature, size and reliance that businesses have on other businesses to perform their core functions has been one piece of what allows this risk to grow,” North told Insurance Business.
“Without being able to fully assess perhaps an insured's exposure to some of this, we're seeing carriers put guardrails on what they're willing to cover and how much of that risk they're willing to carry on their books.”
North said aggregation risk has become a dominant theme in underwriting discussions, particularly as businesses increasingly rely on a relatively small number of major cloud and software-as-a-service (SaaS) providers. “The same large providers sit behind a heavy, heavy portion of our insureds,” she noted.
The concentration creates a major challenge for cyber insurers because an attack or outage involving one major technology provider could simultaneously disrupt thousands of businesses, potentially generating claims across numerous insured accounts.
Unlike traditional property catastrophes, which are generally concentrated within identifiable geographic areas, systemic cyber events can spread across industries. The interconnectedness also complicates insurers' ability to determine how much exposure they are accumulating through individual policies.
“Cyber risk doesn't have borders,” North said. “There's no way to put a physical fence necessarily around that, and certainly not when there's so much aggregation when it comes to cloud and SaaS vendors.”
Underwriters have several tools available to manage heightened cyber exposures, including pricing, deductibles, exclusions and restrictions on available capacity. However, rather than significantly increasing premiums for businesses with critical third-party dependencies, some carriers are focusing on limiting the amount of risk they are prepared to assume.
“I would say more so than pricing impact or potentially deductibles, we're seeing carriers ask more questions,” North said. “If the underwriter flags that as a potential concern, we are seeing them sort of try to limit their capacity exposure to that risk.”
These restrictions can be particularly consequential for dependent business interruption coverage, which may respond when a covered cyber incident at an outside technology provider disrupts an insured's operations. Insurers are increasingly applying sublimits to that coverage or charging additional premium to restore protection to the policy's full limits.
As scrutiny increases, North said underwriters are looking more closely at businesses' dependence on critical vendors and their ability to continue operating if those providers experience an outage or cyberattack.
“We've gotten hyper-focused on shoring up our insureds' own systems,” she said. “But I think there are going to be more questions around vendor management. What sort of controls are required of those who are accessing your network outside of your own company?”
She added that insurers are increasingly examining compensating controls, including network segregation and restrictions on third-party access.
At the same time, businesses should not assume their contractual agreements with technology providers will necessarily protect them against the financial consequences of a cyber incident. Vendor agreements frequently contain liability limitations and indemnification provisions that favor the service provider.
“Many times we have insureds who assume, ‘There’s a contract in place. It probably protects me.’ That’s not always the case,” said North. “Outsourcing the function doesn't outsource the risk.”