AI adoption has outpaced governance at most businesses worldwide, and the insurance market is now catching up to that gap. Gallagher’s third annual AI Adoption and Risk Benchmarking survey of more than 1,200 companies found 43 percent still lack a formal AI risk management framework. Shadow AI tools, meaning those adopted without company approval or oversight, account for much of that exposure. When something goes wrong, the policies businesses rely on may not respond the way they expect.
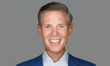
John Farley (pictured), managing director of cyber practice at Gallagher, examines the coverage implications in the interview below. He looks at which policies are most at risk and what businesses need to address before their next renewal.
“Shadow AI creates risk because it puts sensitive data and business decisions outside the company’s established controls,” Farley said.
He points to two specific ways this plays out. Employees can expose confidential information through unapproved tools. Unsupervised AI agents can also take actions without human oversight.
“AI usage brings the potential to trigger multiple insurance policies, including cyber, D&O, general liability, professional liability, employment practices liability, and others,” he said.
But Farley is clear that potential exposure and actual coverage are not the same thing. Coverage depends on the specific facts of each incident and how each policy is worded, he notes. Many existing policies say nothing about AI-driven losses at all, neither confirming coverage nor ruling it out.
“Do not assume an AI-related loss will be covered simply because AI is not expressly excluded,” he said.
Farley argues that the starting point is an AI inventory. Leadership needs to know which tools are in use, what data each can access, and who approves new ones. How tools are tested and how outputs are monitored after deployment also matter. Human oversight should be a core control, not an afterthought.
“Ultimately, it is all about accountability, and that can’t be delegated into ambiguity,” he said. “If ownership of AI risk is unclear internally, it will be difficult to explain to underwriters and transfer that risk effectively to insurers.”
AI governance is now scrutinized in the underwriting process. Farley notes some carriers offer tier-based pricing and adjust available limits based on how applicants respond to AI governance questions.
Sub-limits are also a factor. An insured may not receive full policy limits for AI-driven losses, even when a policy provides coverage. Governance posture determines access to newer endorsements as well.
“This could impact new coverage offerings such as AI voluntary shutdown or AI regulatory risk endorsements,” Farley said.
The biggest mistake businesses make is allowing AI adoption to move faster than AI risk management, Farley explains.
Competitive pressure and the drive for efficiency pushed many organizations into early AI adoption. Many now face exposure across multiple policy lines with no framework in place to manage it.
“Many organizations were pushed into AI adoption to remain competitive and to become more efficient,” Farley said. “That pressure meant that many organizations are now left exposed to what could be a wide variety of losses impacting multiple policies.”
He recommends a thorough review of all potentially impacted policies before the next renewal. The focus should cover three areas: affirmative AI coverage language, coverage constriction clauses for AI-driven losses, and policy silence on the AI peril.
Farley distills the stakes into one question: “If our AI systems fail or cause harm to a third party today, what are the financial impacts to our organization tomorrow?”