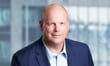
Cyber insurance premiums are dropping even though AI is making attacks quicker, cheaper and simpler to launch, a disconnect brokers should help clients understand, according to Neal Jardine (pictured), chief operating officer and president of BOXX Insurance Canada.
“Basically, the distinction is that premium is falling, yet the risk is going up,” Jardine said at BOXX’s CyberCon event for brokers. “Is that sustainable in the long term?”
Premium levels are largely a byproduct of market capacity and the reinsurance available, he said, so brokers should focus clients on the value of their cover and the services that come with it, rather than price alone.
Read more: Brokers should stop asking clients if they use AI and start asking how, CFC exec says
“AI has fundamentally changed how we live and work, and the pace of that change is accelerating,” Jardine said.
Cybercriminals’ motives haven’t changed, Jardine said.
“At the end of the day, it all comes back to money,” he said.
What has changed is how they operate. Criminal groups now run like corporations, with recruitment teams and bonuses for members who break into systems or negotiate a favourable ransom, he said.
“Cybercrime has become a business in its own right, with organized operations, specialized roles and financial incentives,” Jardine said.
AI is now doing much of their work for them. For years, he said, the saving grace with ransomware was that attackers had to find a vulnerability and then work out how to exploit it.
“AI is helping attackers discover and exploit vulnerabilities, allowing less sophisticated criminals to launch attacks at a scale that previously required much greater technical expertise,” Jardine said.
As a result, the market is swinging back toward ransomware as a key driver of claims costs after several years in which financial crime and fraud dominated, he said. In one BOXX claim, unsophisticated attackers used ransomware-as-a-service software to scan a client, find a password exposed online, then were able to break in through a digital back door and demanded a $2 million ransom. The bigger loss was the downtime: the online retailer was offline for roughly two to three weeks, shortly after announcing it would close its stores and focus on online sales.
Criminals also have an edge in how they use AI, Jardine said. Insurers and businesses work under AI governance policies and privacy legislation, and their tools are restricted, while criminals run jailbroken models with no limits.
“While legitimate businesses must balance AI innovation with governance, privacy and regulation, cybercriminals face none of those constraints. That creates a significant advantage in how quickly they can adopt and exploit emerging technologies,” he said.
Social engineering is the most frequent type of attack BOXX sees, Jardine said, and AI is making it far harder to spot. Phishing emails no longer give themselves away with typos or poor grammar.
In one claim, attackers created an entire fake email chain between a company president and a friend arranging a round of golf, he said. The chain ended with the friend asking to send an invoice for penetration testing straight to accounting. An employee in accounting, knowing the two golfed together, paid it without checking.
Criminals once had to comb through Facebook and LinkedIn to find those relationships, Jardine said. Now AI can identify two friends in positions of authority at an organization.
In another case, a law firm fell for a tech support scam, he said. An attacker called through Microsoft Teams under the display name “Technical Support,” and the lawyer handed over access. The attacker then changed banking details and redirected settlement funds meant for a motor vehicle accident claimant.
Cyber risk is also no longer contained within a single company, Jardine said. Most small and mid-sized businesses rely on the same handful of cloud providers and software platforms, and attackers increasingly go after those suppliers.
“They're not necessarily breaking into the company itself. They're targeting the technology providers that the company depends on,” he said.
He pointed to the 2024 attack on CDK Global, a software provider whose outage shut down car dealerships across Canada and the U.S. and produced large business interruption claims. Downtime can also stretch well beyond the system restore, he said. One client’s digital printers took about a week to recalibrate, and an injection moulding client had to ship out machines after plastic cooled inside them.
That makes one question essential for brokers, Jardine said.
“How dependent are you on other technologies?” he said. “Everyone’s dependent on someone else.”
Read more: If a fridge can be hacked, insurers should brace for a bigger surprise, Aviva exec warns
Brokers should ask clients which technologies they depend on most and how an outage at any of them would affect the business, he said. If a client can’t say which vendor could knock it offline for two weeks, “that’s a bigger problem.”
And small businesses are the most exposed, Jardine warned. There are only a few thousand large corporations worldwide but hundreds of millions of SMEs, most with fewer controls.
“There are millions of small businesses, and when they’re hit by cyberattacks, the cumulative impact on the economy can be significant,” he said.
Jardine said technology should free brokers from paperwork so they can spend their time advising clients.
“As brokers, I don’t think you should be focused on filling out insurance applications,” he said. “Brokers should be advising clients on a risk management approach that’s in scope with their needs.”
A business with heavy technology dependence may need contingent business interruption cover, he said, while a small paint shop with few systems is more exposed to financial crime and fraud. On limits, he suggested brokers ask clients about their largest and average payments and what controls sit around them.
He also urged brokers to consider bringing in a PR firm early when a client experiences a cyber incident. At approximately $10,000 to $15,000 on a million-dollar claim, proactive communications support can help protect a client's reputation and manage the potential fallout, he said.
Above all, Jardine said, clients should call their insurer early rather than wait until the damage is done. Approximately 80% of the cyber incidents handled by BOXX's Hackbusters team are resolved before they develop into insurance claims, he said. Unlike traditional insurers that step in only once a claim is filed, he said, insurtechs also offer preventive support, including scanning and monitoring clients’ systems and taking their calls whenever they have a concern.
“Cyber insurance shouldn't be something that clients and brokers turn to when things go wrong. Insurers can play an active role in helping businesses understand risks and preventing incidents before they escalate with expert support,” Jardine said.