Many cyber incidents begin not with a sophisticated hack but with something that could have been prevented, such as a password left exposed on the dark web or a message sent to an employee’s personal phone, according to BOXX Insurance’s technology leaders.
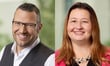
Speaking at BOXX’s CyberCon event for brokers, Steve Penney (pictured right), chief technology officer at BOXX Insurance, said incidents can often start with a stolen password that was never changed or a WhatsApp message sent to someone’s personal device.
“Those are preventable human issues,” Penney said.
Read more: Cyber premiums are falling as AI drives risk higher
At the same time, attackers have become increasingly efficient, no longer needing to develop their own tools to carry out attacks.
“Ransomware has been industrialized,” Penney said. “They’re not building software from scratch. They’re using AI and automation to hack.”
Social engineering and funds transfer fraud have also increased sharply. Members of BOXX’s own executive team have received payment requests through links in WhatsApp and during Zoom calls, illustrating how criminals are exploiting familiar communication channels.
“The channels are getting pretty creative,” Penney said.
The growing volume of software vulnerabilities is creating another challenge for businesses trying to distinguish genuine threats from background noise. The number of disclosed vulnerabilities has increased dramatically, Penney said, but only a small share have a proven exploit. For businesses and their insurers, that means “a ton more noise,” even as some vulnerabilities require urgent attention.
That makes it increasingly difficult to rely on a snapshot of a company's security posture. A scan conducted at quote time, followed by a vulnerability report that sits untouched until renewal, may no longer reflect how quickly new threats emerge during the policy period, Penney said.
Read more: Brokers should stop asking clients if they use AI and start asking how
He identified several indicators that can help businesses understand where they are most exposed. Staff credentials appearing online, for example, can signal a potential business email compromise attack, while known vulnerabilities matched to a company's systems can point to ransomware risks. Exposed services, including open remote desktop connections or unprotected VPNs, can provide attackers with an easy entry point because “it doesn’t take a very skilled hacker to get in there,” he said.
Other warning signs may be less obvious. Lookalike domains can be registered to impersonate a business and send fraudulent invoices. BOXX was alerted after someone registered a copycat version of its own domain, Penney said. Weak email security settings can create a similar problem by allowing criminals to send convincing messages that appear to come from a company's own domain.
But even with these technical indicators in view, the hardest risk to manage remains human behaviour, which is why BOXX runs phishing simulations and training every month.
That vulnerability is particularly evident in how employees manage passwords, said Marcus Fluellon (pictured left), cybersecurity lead at BOXX. Password reuse remains one of the most common weaknesses he encounters, with employees using the same credentials across work and personal accounts.
“Employees reuse their password across different business and personal accounts,” Fluellon said.
The problem is especially acute among small businesses, where the same credentials can remain in use across multiple accounts for years.
The risks are also evolving as artificial intelligence gives businesses and attackers new capabilities. To demonstrate how quickly the technology is changing cybersecurity, Penney described an AI-driven deep scanning tool BOXX built to probe a company's systems in much the same way an attacker might. The scans are run only at the request and with the consent of the broker and the insured, Fluellon said.
The tool demonstrated how accessible this kind of technology has become. It did not cost millions to develop, Penney said.
Read more: Personal cyber cover is playing catch-up as most Canadians don’t know it exists
“It’s something that was done all together in a couple of weeks with a couple of AI prompts,” he said.
In one case, a deep scan of an e-commerce client uncovered a flaw that would have allowed anyone to generate gift cards of any value on its website, Fluellon said.
“Thankfully, we caught that before anything happened, and the insured was able to fix that vulnerability,” he said.
For BOXX, identifying vulnerabilities is intended to help businesses address weaknesses before they become losses, rather than give the insurer grounds to avoid a risk.
That approach also shapes what brokers should be discussing with clients, Penney said. Beyond whether a business has cyber coverage, brokers should ask what the policy does when a serious vulnerability emerges mid-term, how the business will know if employee credentials appear in a data leak, and what its systems look like from an attacker's perspective.
“The market is moving fast,” Fluellon concluded.