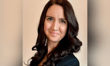
Insurers are likely to respond to artificial intelligence risk first by excluding it, before competition pushes the market toward dedicated AI coverage, according to Virginie Boucher (pictured), senior vice-president, Quebec division, at CHES Special Risk.
Many insurers still have no AI exclusions in their wordings, Boucher told Insurance Business, though underwriters are asking more questions about how clients use the technology. As claims emerge, she expects exclusions to be the first move, which she described as “the easy way” for insurers to limit their exposure.
Read more: Kidnap and ransom insurance demand has broadened well beyond high-risk travel
Once some insurers exclude AI, others will adapt their wordings to cover it, and dedicated products will follow, Boucher said. She compared it to the way cyber developed as a new line about 10 years ago, but said AI will move much faster.
Within five years, Boucher expects the market to offer three distinct approaches, either built into existing policies or sold separately. A simple exclusion may work for a business that doesn’t rely on AI, while technology companies will need wordings adapted to how they use it, within set boundaries. Dedicated policies could eventually cover AI the way cyber policies cover digital risks today.
The challenge for insurers will be defining what they are actually covering, particularly as AI becomes embedded in existing business operations rather than remaining a separate technology. A company may use AI for relatively straightforward administrative tasks, while another may depend on it for services or decisions that carry greater financial or operational consequences. Those differences could make a single, broad approach to AI exclusions difficult to sustain as the market develops.
Boucher said she has already seen two insurers developing AI products. When brokers asked what the main claims would look like, neither could say, because the risk is so new.
AI is a useful tool for technology companies, Boucher said, for example, in speeding up translation and review work at a lower cost. The danger comes when it runs without oversight, she said. Systems operating on their own can produce hallucinations, as chatbots have shown, and “you lose control.”
“You still need the human revision behind that,” Boucher said.
Insurers will need to understand where problems could arise, she said, because AI now touches cars, homes, computers and employees.
“That’s very productive, but we’re going to have to be very careful,” Boucher said.
The broader cyber market is in a strong position for buyers, Boucher said, with increased insurer capacity and greater familiarity with cyber risks helping to create a more competitive environment.
“Honestly, cyber actually seems to be more stable than the last five years, but it’s still very competitive,” she said.
More insurers understand cyber and have entered the market, adding capacity and putting downward pressure on prices. At the same time, insurers are expanding their offerings beyond full cyber policies, introducing options such as cyber extensions and small-limit products to reach businesses with different coverage needs.
With more products available, the differences increasingly come down to the details of the coverage, Boucher said. Sublimits are now one of the main points of distinction between policies, while cyber crime protection has become a common feature. For brokers, that means looking beyond the availability and price of a policy to assess how well its coverage responds to a client's particular exposures.
Most products now include cyber crime cover, “and that’s what the customer is looking for,” she said.
Read more: Depreciated payouts are leaving contractors owing more than their wrecked equipment is worth
For 2027, Boucher expects pricing to remain flat for most risks, although she sees a different outlook for healthcare, government and aviation. Claims in those sectors are frequent and expensive, she said, putting them under greater pressure. Healthcare is particularly exposed because health data is highly valuable on the dark web, making the sector an attractive target for cyber criminals.
The nature of cyber losses has also shifted, Boucher said. Five years ago, attacks tended to be large, direct, one-time events. Now criminals target individual employees, mainly through phishing emails, looking for a single way in.
Most large companies now train their staff, and employees are more willing to tell their IT team when they think they have made a mistake, she said. But no filter catches everything, and “sometimes we are just tired,” Boucher said.
That makes a cyber policy’s incident response line one of its most valuable features, she said, because in the first hour after an attack, a business can lose control of the situation entirely.