Canada’s cyber insurance market still has plenty of capacity and stable pricing, but brokers and insurers expect conditions to tighten within the next year as AI speeds up attacks and legal exposure grows, according to panellists at BOXX Insurance's CyberCon event.
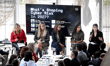
Sophia Kudlyk (pictured centre left), senior vice-president, cyber and technology, at HUB International, said brokers currently face no difficulty placing cyber risks, with domestic capacity “still very ample, which is good news.” But she has been warning clients that conditions will change.
Read more: Insurers will exclude AI before they cover it, CHES SVP says
“I think something bigger than this, bigger than us, bigger than what we understand is coming,” Kudlyk said on the panel, titled What’s Shaping Cyber Risk in 2027?
Rising frequency, vendor risk, aggregation, widespread events and AI are combining into a “perfect storm,” she said.
“We’re not seeing it hit yet, but I would be really shocked and surprised if we don’t see it in the next six months to a year,” Kudlyk said.
Ruby Rai (pictured centre), cyber practice leader, Canada, at Marsh, said brokers are also having no trouble securing cover, “which is scary.”
Some industries, such as manufacturing, face more scrutiny than before, she said. And while clients benefit from soft conditions, “there is advantage in a stable market,” Rai said, because it helps insurers adapt the product as cyber risk transfer needs will continue to broaden and evolve.
“I wouldn’t call it hard yet,” Rai said.
Avi Mali (pictured centre right), head of cyber, Canada and Middle East, at Zurich Canada, said Canada typically trails the U.S. market by “six to eight months” on rates. In the U.S., cyber pricing has steadied.
“The US market has been stabilizing the last few months now, so they’re pretty much flat on a rate basis,” Mali said.
She said she expects Canada to follow within about a year.
Kudlyk said the biggest change over the past six months has been the pace of change itself. The AI tools that help businesses become more efficient “are in the hands of cybercriminals as well,” she said. Attackers aren’t necessarily creating new types of claims, but they are much faster at spreading existing threats.
“Better tools and faster speeds lead to more impact and more damage, and I’m just shocked at the pace of it all,” Kudlyk said.
Mouna Hanna (pictured right), partner and Canadian head of the cyber, privacy and data protection group at DWF, said her breach response team has “never been busier.” Law enforcement is also warning more organizations of imminent attacks, she said, sending responders scrambling to contain them before they turn into ransomware.
“AI is not the problem in cyber, but it’s making our previous problems worse,” Hanna said.
Threat actors now move through networks faster, find critical data and take it out quickly, she said. Ransom negotiations increasingly start with an AI chatbot giving scripted responses, which grows more aggressive at any sign of delay, along with AI-driven robocalls to the victim organization.
Read more: AI lets scammers turn one data breach into thousands of targets, Aviva expert says
“The attacks are much worse versus 5, 7 years ago,” she said.
For insurers, AI also adds a layer of systemic risk, Mali said. Clients already depend on managed service providers and third-party vendors, and the growing concentration of AI services among a small number of providers and hyperscalers creates another potential point of systemic exposure.
Mali said Zurich has seen an increase in claim notifications over the past couple of months. A widely reported PHP vulnerability generated some notices, she said, because “about 80% of companies use PHP for internet-facing websites,” but relatively few actual breaches. Retail, manufacturing and professional services remain the classes most exposed to ransomware and email compromise.
Clients that are open with their insurer during a claim tend to improve afterwards, Mali said.
“We’ve seen that our clients that are more transparent, they do invest more in the controls in the year after,” she said.
Hanna said the next big shift in Canada is likely to be legal.
“What I can predict is coming, probably like a fast-moving train, is the increased rate of class actions here in Canada,” she said.
In the U.S., class actions are now being filed on behalf of fewer than 10,000 people, Hanna said, “so it’s not these massive class actions anymore,” and some are launched within two weeks of a breach becoming public.
“My expectation is that we’re going to see that trend come down to Canada,” she said.
That means organizations need the forensic capability to show exactly what data was affected, Hanna said, because “gone are the days where you keep it general.” Third parties are also making more frequent and larger demands to be reimbursed for incident costs, she said.
Read more: Fridge hacks and Binance expose cyber cover gap as premiums climb
Regulators are tightening too. Federal privacy reform has repeatedly stalled, Hanna said, but fragmented changes are adding pressure, and regulators now ask not only what an organization did after an incident, but “what did you do beforehand?” Ontario’s privacy commissioner has also begun issuing fines under the province’s health information law. The two fines so far are small, but they show a regulator “starting to flex the muscles a little bit,” Hanna said.
Rai said many incidents could be avoided with the right controls, putting the estimate at roughly 50% to 60% of what insurers pay out. Widespread events such as mass vulnerabilities aren’t necessarily catastrophic, she said, but “these are widespread events that exhaust the ecosystem.”
“It’s imperative that organizations consistently improve baseline controls to prevent avoidable incidents, not only to reduce frequency of events but to be ready for evolving risks that are ahead,” Rai said.
Brett Boadway (pictured left), executive director of CAMGA, who moderated the panel, said insurance requirements are already pushing businesses to improve their security. The insurance industry is “acting as a natural market force to get businesses to adopt cyber best practices,” Boadway said, adding that “you don’t need a regulator or a law change to force folks to make the right decisions for their business.”
For brokers, the job is expanding beyond placing cover, Kudlyk said. With clients flooded by vulnerability alerts from multiple carriers, brokers must decide “where do we draw the line between adding fuel to the fire and alerting what is really severe and important for the client to understand.”
She said brokers should use the current market to build up clients’ risk management and broaden the conversation beyond risk transfer, so they are ready when conditions turn.
“I think it’s undeniable. It’s just a question of when,” Kudlyk concluded.